



A security posture that adapts to the risk of each identity
Identity Guard conducts SASETY's 5 security technologies: it brings their signals together, assesses the risk of each identity and coordinates the response across all technologies at once. Then it gradually brings protection back to normal.
Attackers no longer break in. They log in.
+32 %
increase in identity-based attacks in H1 2025
97 %
of identity attacks target passwords
22 %
of breaches start with stolen or misused credentials
6 167
breaches notified to the CNIL in 2025 (+9.5% in one year)
A continuous loop, 24/7
Detection, immediate hardening, remediation, then a controlled return to normal.
Assess
Each identity receives a DEFCON score. Signals from the 5 technologies and Entra ID, correlated continuously.
Trigger
Protection evolves with risk. Graduated, targeted measures, orchestrated through APIs.
Verify
Remediation is proven.
Restore
The user gets access back. Controls relaxed, gradual return to trust.
Technologies that work together, orchestrated by Identity Guard
With SASETY, the 5 technologies share their signals with Identity Guard, which decides on the response and has it applied consistently everywhere, through APIs, within minutes.
Identity GuardCorrelates signals · calculates the DEFCON score · orchestrates the response


Graduated, targeted and reversible measures
Constraints apply only to the identity concerned, for as long as needed.
One alert detected, every technology mobilises to protect the digital identity
Then Identity Guard verifies remediation and restores trust, step by step.
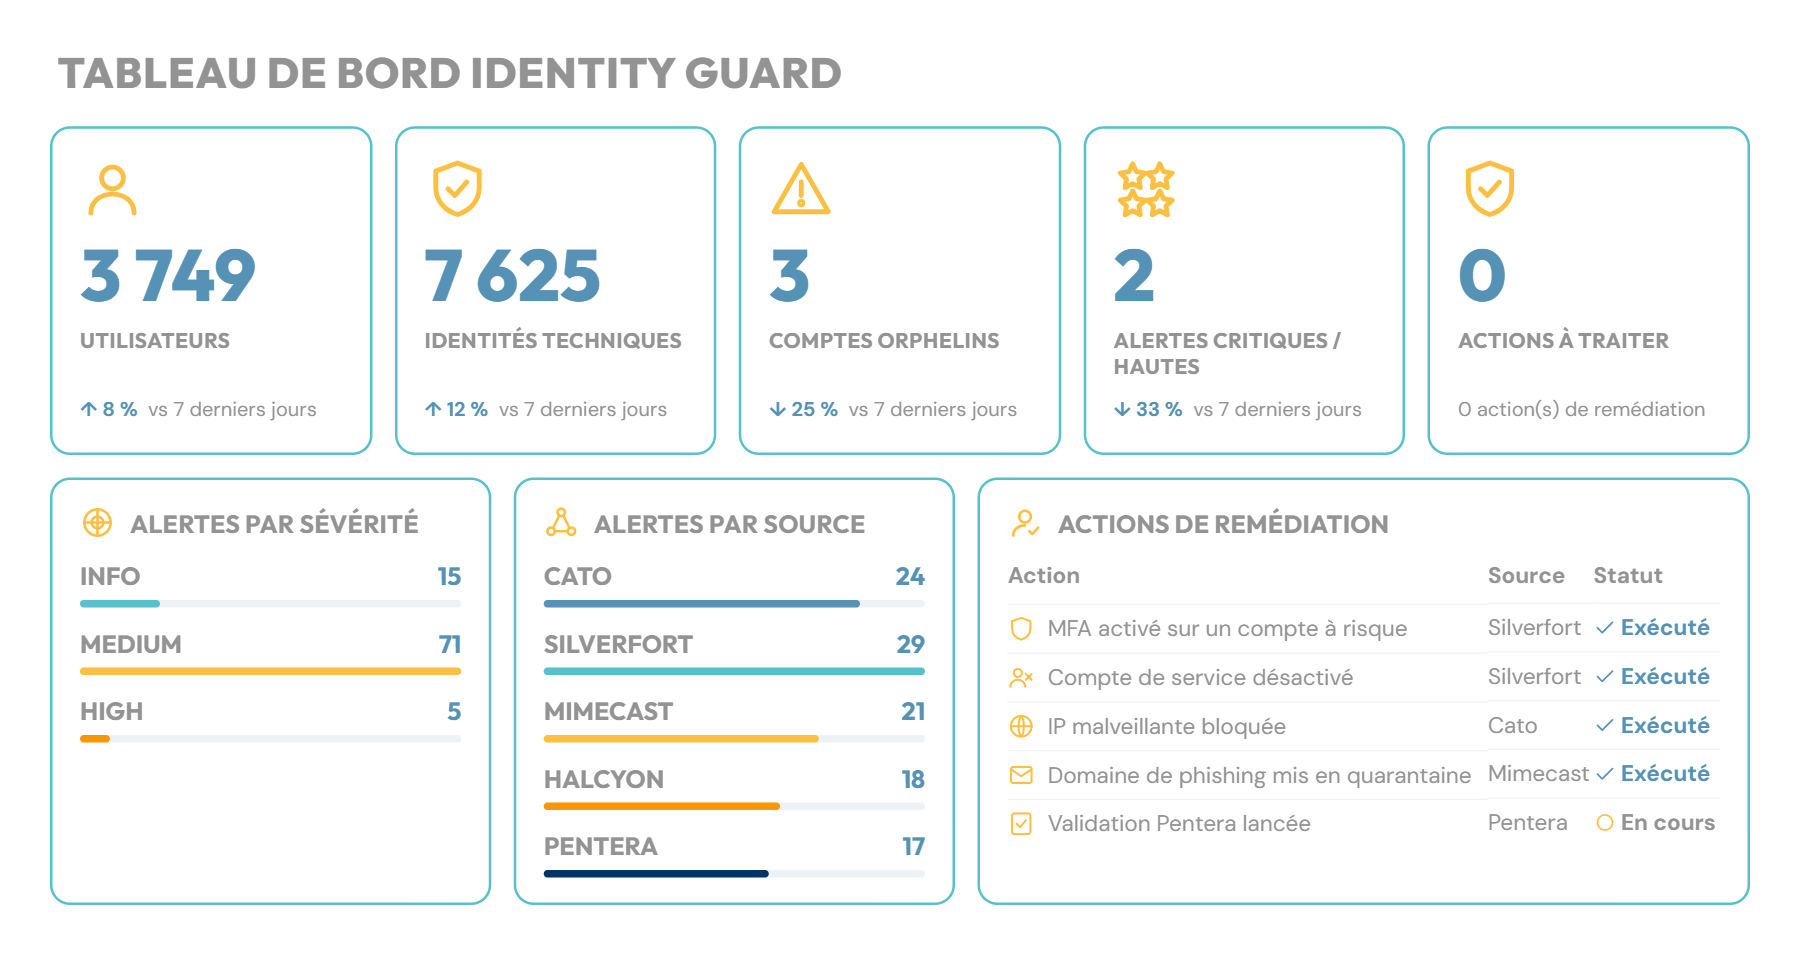
The risk of each identity, clear at a glance
- DEFCON score per identity and trend over time
- Weak signals and alerts consolidated from the 5 technologies
- Measures applied, remediation and return to normal tracked step by step
- A shared view for internal teams and our experts
“The SOC sees the alert. Identity Guard understands the identity, measures its risk and adapts its protection.”
Client SOC
Detect & investigate
- Monitor the entire IT estate
- Correlate alerts
- Qualify incidents
- Lead the overall response
Identity Guard
Adapt protection
- Consolidate risk per identity
- Contextualise by role and usage
- Orchestrate coordinated controls and actions across the 5 technologies
Reduced risk
The SOC keeps the overall view. Identity Guard tracks remediation and manages the gradual return to trust.
Between “let everything through” and “shut everything down”
Graduated response
Steps between “let everything through” and “shut everything down”.
Action in minutes
Decisions orchestrated and applied automatically across technologies.
Less noise
Moderate risk is handled, internal teams focus on what matters.
Back to normal
Less friction for users and fewer support tickets.
A step‑by‑step approach
Scoping workshop, prioritised protection plan, then continuous operations.